Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site – Krebs on Security

The U.S. federal investigation into the cybercriminal collective known as ShinyHunters has taken a dramatic turn, revealing that the barrier between legitimate incident response and criminal enterprise has been dangerously breached. Law enforcement agencies, led by the FBI, have identified executives at multiple ransomware negotiation firms who allegedly maintained clandestine, symbiotic relationships with the hackers. These relationships, described by investigators as "unusually close," involve not merely the facilitation of payments, but the active operational support of the group’s extortion infrastructure, including the management of victim-shaming websites.
The Rise of the ShinyHunters Syndicate
Since its emergence in 2019, ShinyHunters has evolved from a small group of cybercriminals primarily operating out of France into a global juggernaut of data extortion. Following the steady attrition of its original leadership through international law enforcement efforts, the group’s brand was revitalized under the command of an individual identified as "Rey," a teenage hacker based in Amman, Jordan.
According to FBI estimates, the syndicate has successfully extorted more than $70 million from victims in the current year alone. The group’s reach expanded significantly in September 2026, when they executed a brazen cyberattack on the FBI recruitment portal, fbijobs.gov. By accessing sensitive data—including psychological evaluations, home addresses, and internal unit designations of personnel—the group signaled a new level of audacity. This provocation accelerated the FBI’s pursuit, leading to the October 3, 2026, detention of Rey by Jordanian authorities, who is currently cooperating with American investigators.

Chronology of a Criminal Network
The unmasking of the group’s internal operations followed the high-profile arrest of Pepijn van der Stap, a convicted hacker apprehended in the Netherlands on September 15, 2026. Dutch law enforcement executed the arrest using specialized tactical methods while Van der Stap was actively logged into his encrypted messaging accounts.
The subsequent forensic analysis of Van der Stap’s Signal account provided investigators with a roadmap of the group’s international reach. These messages reportedly contained communications with ransomware negotiators based in both Canada and the United States. Crucially, the digital trail uncovered by authorities suggests that Van der Stap had orchestrated a potential murder-for-hire plot, an alarming development that highlights the violent potential inherent in modern digital extortion. While there is no evidence that these specific orders were executed, the intent underscores the shift from mere data theft to aggressive, real-world criminal behavior.
The Alleged Role of Ransomware Negotiators
On October 9, 2026, the investigation reached a critical milestone with the arrest of Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive. Dubrovsky, who had previously authored professional literature advocating for proactive engagement with ransomware actors, faces federal charges, including the threat to disclose stolen data and interference with interstate commerce. Prosecutors have argued for his continued detention, noting the severity of the alleged collusion.
Evidence suggests that the cooperation between these executives and the hackers was not a one-off occurrence. Investigators have uncovered communication logs showing that individuals like Dubrovsky were often briefed on the details of new victims before those victims were even aware they had been compromised. Perhaps most damning is the evidence suggesting that Dubrovsky was aware of the breach of FBI servers but failed to notify the bureau, effectively allowing the hackers to maintain their leverage until they chose to publicize the attack on social media platforms.

The Infrastructure of Extortion: Shinywire
Perhaps the most significant revelation in the investigation is the existence of "shinywire[.]com," a website dedicated to pressuring organizations into paying ransoms. Investigators believe that at least one executive at a prestigious U.S.-based consulting firm—a company with over 1,000 employees—played an active role in the operation of this platform.
The Shinywire site served as a digital pressure cooker, listing nearly 100 organizations compromised by ShinyHunters. Each entry provided victims with specific instructions on how to initiate payment negotiations and featured samples of stolen data as a warning of what would happen if demands were ignored. The site functioned from May 3, 2026, until its seizure on October 16, 2026. The targeting of major entities, such as the medical technology firm Intuitive Surgical, illustrates the group’s willingness to disrupt critical infrastructure to maximize financial gain.
Industry Conflict and Ethical Fractures
The involvement of professional negotiators in criminal schemes highlights an inherent conflict of interest within the cybersecurity industry. Many firms operate on a model where the negotiator’s compensation is tied to a percentage of the final ransom payment. As industry experts like Mark Camillo, CEO of CyberAcuView, have noted, this structure creates a perverse incentive for negotiators to prioritize the payment of ransoms rather than pursuing alternative recovery strategies.
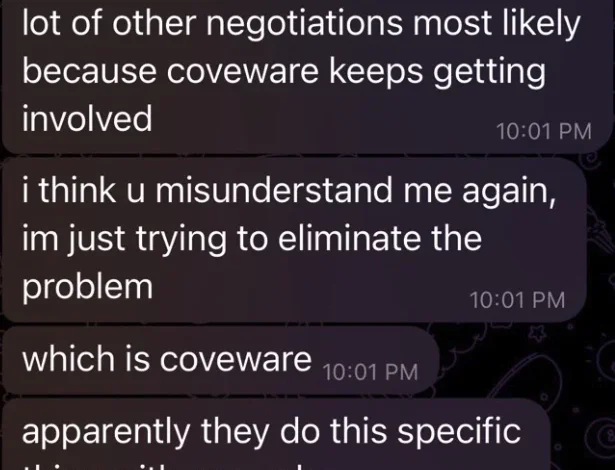
This alignment of interests has been further evidenced by the aggressive tactics used by ShinyHunters against firms that counsel victims against paying. Internal communications from the group’s Telegram channels show members explicitly naming and disparaging incident response companies like Coveware and Unit 221B for their "misinformation"—a term the hackers use for advice that discourages ransom payments. The hackers viewed these firms as a direct threat to their business model and discussed strategies to "eliminate" their influence in the marketplace.

Broader Implications for Cybersecurity Policy
The legal landscape is shifting rapidly as the Department of Justice intensifies its crackdown on "double-dealing" negotiators. Recent cases, such as the prosecution of MonsterCloud CEO Zohar Pinhasi and the sentencing of Angelo Martino, indicate that the U.S. government is no longer willing to view ransom facilitation as a neutral service.
The case of PowerSchool, which paid a $2.85 million ransom only to find the stolen data being resold and used in subsequent extortion attempts, serves as a grim reminder of the futility of paying criminal groups. The breach, which exposed the private information of 62 million students and 9.5 million teachers, underscores the reality that there is no technical or moral guarantee when dealing with entities like ShinyHunters.
Conclusion and Future Outlook
The collapse of the relationship between legitimate cybersecurity professionals and the ShinyHunters collective represents a significant turning point in the fight against ransomware. As federal investigators continue to comb through the digital evidence provided by the arrests of Van der Stap, Dubrovsky, and others, the industry faces a reckoning.
The expectation of transparency and the separation of negotiation from remediation will likely become the new standard for corporate incident response. For organizations, the lesson is clear: the path to recovery cannot be paved with payments to those who hold the keys to their own digital demise. The ongoing investigations into these executives will likely lead to further indictments, signaling that the era of impunity for those who bridge the gap between cybersecurity defense and criminal extortion is rapidly coming to an end. The cooperation of key figures like "Rey" suggests that the authorities have gained a deep, inside view of how these networks operate, which will likely yield further disruptions to the global cyber-extortion landscape in the coming months.