Google Dismantles Massive Android TV Botnet XCPE Linked to Chinese Manufacturer Videostrong Technology Co

In a significant operation targeting the intersection of consumer electronics and cybercrime, Google, in collaboration with global industry partners, has successfully dismantled the XCPE botnet. This sprawling digital infrastructure comprised more than 1.3 million compromised Android TV set-top boxes, which were pre-infected with malicious software at the point of manufacture. The malware, identified by the Google Threat Intelligence Group (GTIG), covertly transformed these devices into nodes for a "residential proxy" network, enabling unauthorized third parties to rent user internet connections for advertising fraud, account takeovers, and large-scale data scraping.
Beyond the initial 1.3 million devices, security experts warn that the takedown has severed connectivity to an estimated 10 million additional compromised systems, including a variety of Internet of Things (IoT) hardware such as karaoke machines, digital signage systems, and sensitive telehealth devices. This operation marks a pivotal moment in the ongoing battle against the weaponization of low-cost IoT hardware, highlighting a critical breach of trust in the global supply chain.
The Anatomy of the XCPE Botnet
The XCPE botnet was engineered to turn legitimate consumer electronics into unwitting participants in criminal activity. At the heart of the operation was Videostrong Technology Co., a China-based manufacturer. GTIG’s investigation revealed that Videostrong deliberately embedded malicious code into the firmware of their devices. This malware, named "XCPE" after a core code component, was designed to execute immediately upon the device’s initial boot-up.
Once active, the XCPE software effectively hijacked the device’s internet traffic. By making the user’s IP address available to residential proxy services, the botnet allowed external users to mask their true locations and web traffic. These proxy services are frequently exploited by malicious actors to bypass security filters, engage in mass content scraping for AI model training, and perform sophisticated advertising fraud. According to the investigation, Videostrong monetized this backdoor by selling access to the infected device network to various criminal affiliates, who then deployed additional malware modules to further exploit the hardware.

Chronology of Discovery and Takedown
The identification and subsequent neutralization of the XCPE botnet followed a string of research efforts that began in early 2026.
- January 2026: Security startup Synthient published groundbreaking research on the "Kimwolf" botnet, which had been utilizing similar vulnerabilities to orchestrate massive Distributed Denial of Service (DDoS) attacks. This research alerted the industry to the rapid, automated infection of Android set-top boxes.
- June 2026: Federal authorities, including the FBI, acted against the "Popa" botnet, seizing hundreds of domains associated with the Israeli company Alarum Technologies (NetNut). This operation provided early insights into how residential proxy providers were being used to enslave TV boxes.
- October 2026: Oxylabs and Honeygain were reorganized under the "Source" brand, following a $130 million funding round. During this period, scrutiny of residential proxy networks intensified as their role in global cyber-attacks became more apparent.
- November 2026: Google officially announced the successful legal action taken against the domains and command-and-control servers utilized by Videostrong. The coordinated effort involved multiple security firms, including Synthient, to track and neutralize the infrastructure.
The Role of Residential Proxy Providers
The GTIG report identified several residential proxy providers whose Software Development Kits (SDKs) were consistently found on devices infected by XCPE. These entities provide the marketplace where the stolen bandwidth is bought and sold. Among those named are AppSalt (Honeygain), NetNut, EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, and GaGaNode.
The involvement of these providers has sparked a debate regarding accountability. While many of these firms claim their services are intended for legitimate web scraping and market research, the investigation proves that their infrastructure is being abused by bad actors who exploit the lax verification of "consent" flows. In response to the revelations, Oxylabs stated that while they require user consent, developers often fake these signals. The company pledged to improve its "build fingerprinting" to prevent the use of its SDKs on unauthorized, pre-infected builds.
Industry Impact and Consumer Vulnerability
The scale of this operation is, according to experts, "highly conservative." Synthient founder Ben Brundage emphasized that the 1.3 million figure represents only a portion of the total devices affected. Because many of these set-top boxes are marketed through social media influencers and sold on platforms like Amazon or via direct-to-consumer websites, they often reach households without the users ever suspecting that their home network has become a staging ground for criminal activity.
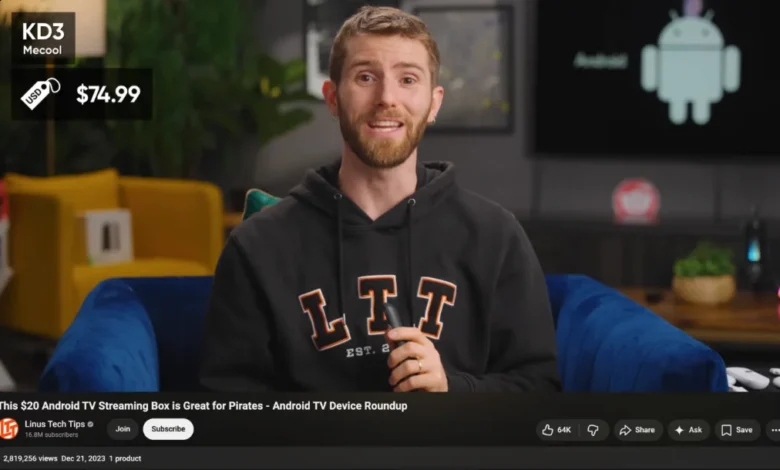
A prime example of this distribution model is the MECOOL brand of TV boxes, manufactured by Skyworth Technology. Synthient’s research revealed that these devices were bundled with the same Videostrong-originated malware. The popularity of such devices often surged after being featured by high-profile technology YouTubers, who—often unknowingly—promoted the devices for their ability to stream pirated content for a one-time fee. While channels like Linus Tech Tips have since updated their content to warn users and remove affiliate links, the damage remains embedded in the millions of units already deployed in homes globally.

Security Implications and Future Outlook
The XCPE takedown underscores a systemic failure in the Android TV ecosystem. Although Google enforces compatibility and security tests for Android device manufacturers, the "bad actor" manufacturers found ways to inject malicious code post-factory or through unauthorized firmware modifications that bypassed initial checks. Google has stated that it has since addressed the specific weaknesses that allowed this code to execute at boot, but the sheer volume of existing, unpatched hardware remains a concern.
The broader implications are sobering. When a manufacturer turns its own product into a threat, the traditional security model—which relies on the integrity of the device’s operating system—collapses. For consumers, the shift from a secure device to a botnet node is invisible. There are no performance drops or obvious error messages; the device continues to stream media while simultaneously exfiltrating data or facilitating illegal web traffic in the background.
Moving forward, the security community is calling for stricter supply-chain auditing and a more rigorous approach to the "residential proxy" industry. By fragmenting the botnet, the recent takedown has significantly reduced the capacity for large-scale DDoS attacks and criminal traffic. However, as long as there is a profitable market for residential IP addresses, the incentive for manufacturers to create "backdoored" hardware persists.
Conclusion
The dismantling of the XCPE botnet is a significant victory for digital safety, but it serves as a stark reminder of the hidden dangers lurking in the "Smart Home." As consumers continue to integrate increasingly cheap, unverified IoT devices into their local networks, they become part of a global infrastructure of exploitation. The cooperation between Google, law enforcement, and independent researchers like Synthient is essential, but it is only one piece of the puzzle. Without greater transparency from proxy providers and stricter accountability for hardware manufacturers, the cycle of compromise, detection, and remediation is likely to continue. Users are advised to avoid "off-brand" streaming boxes that offer unauthorized access to premium content, as these devices are the primary vectors for such malware, posing not only a legal risk but a severe, ongoing threat to the security of their private home networks.
Related posts: