FBI sting operation exposes ransomware remediation firm as fraudulent operation built on double-dealing

In a chilling case of professional betrayal, federal authorities have dismantled a Florida-based cybersecurity firm that masqueraded as a savior for victims of ransomware while secretly operating as an extortion middleman. Juan Ricardo Palacio Escobar, the 52-year-old co-founder and Chief Technology Officer of RansomwareHelp, now faces federal wire fraud charges after an FBI sting operation revealed that the company’s touted "advanced cryptographic tools" were a complete fabrication. Instead of using proprietary technology to decrypt files, Palacio allegedly paid off cybercriminals behind the scenes and pocketed a significant markup from desperate victims, effectively victimizing companies twice over.
The indictment, unsealed this week in Rhode Island, pulls back the curtain on a sophisticated facade that had been operating for six years. RansomwareHelp marketed itself as a high-end, ethical remediation firm, explicitly promising clients that it would never negotiate with or pay threat actors. Yet, the investigation suggests that the company’s business model relied entirely on the very thing it claimed to oppose: fueling the ransomware economy by facilitating payments.
The Anatomy of a Deception
RansomwareHelp maintained a polished digital presence designed to instill confidence in organizations facing existential threats. Its website boasted a staff of 80 experts and claimed 28 years of experience in fields ranging from forensic analysis to reverse engineering. The site featured bold headers urging victims, "Do not pay the ransom!" and promised a 99 percent success rate through "proprietary tools and algorithms" that could restore systems to their original state.

In practice, the firm’s methods were significantly less technical. According to the indictment, Palacio acted as a broker for the hackers. When a victim contacted the company, Palacio would conduct a perfunctory diagnostic, then secretly approach the ransomware group to secure a decryption key. Once the key was obtained, he would present the extortion demand to the victim, significantly inflated to include a "service fee" that sometimes amounted to thousands of dollars in excess of the actual ransom.
The FBI Sting Operation
The federal investigation was triggered by a meticulously planned sting operation. FBI agents established a two-pronged deception: they posed as a corporate entity suffering a ransomware attack and simultaneously operated as a fictitious, malicious hacking collective.
The sequence of events was as follows:
- The Initial Contact: The "victim" company contacted RansomwareHelp, reporting a breach and providing a copy of a ransom note.
- The Front: RansomwareHelp responded with its standard script, confirming its policy against paying ransoms and promising to use internal forensic tools to break the encryption.
- The Secret Negotiation: Shortly after, Palacio contacted the "hackers" (the FBI agents) and negotiated the lowest possible price for a decryption key.
- The Markup: When the FBI agents set a price of approximately $13,000 in Bitcoin, Palacio immediately turned to the "victim" company, claiming the decryption process would cost $13,260.
- The Final Fraud: To further maximize his gain, Palacio returned to the fake hackers and haggled the price down to $4,000, ultimately charging the victim firm a total of $16,010, which included a $2,750 "diagnostic fee" on top of the inflated ransom.
Technical Fraud and Network Manipulation
The case highlights how these firms often engaged in active sabotage to keep their clients in the dark. Paul Ihme, co-founder of the security firm Soteria, provided crucial testimony regarding a 2024 investigation into RansomwareHelp. He recounted a scenario where a small accounting firm, panicked by a Lockbit infection, sought help from Palacio’s company.

RansomwareHelp presented a proposal for over $438,000, claiming the use of "510 preconfigured forensic servers" to perform brute-force attacks on the encryption—a claim experts dismiss as technologically illiterate. More nefariously, the firm insisted on "unrestricted remote access" to the victim’s network via Anydesk.
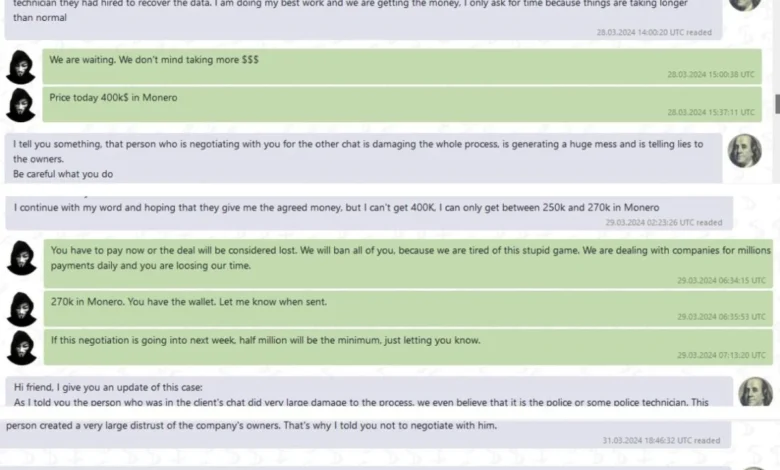
Ihme’s analysis suggests this access was not for repair, but for concealment. By deleting the ransom notes left by the hackers, RansomwareHelp ensured the victim could not contact the attackers directly. When Ihme’s team finally found a backup copy of a ransom note, they discovered that negotiations were already underway between Palacio and the Lockbit group. The attackers, growing frustrated by the convoluted communication chain, threatened to increase the ransom by $100,000 per day due to the interference, effectively holding the victim’s data hostage to a "middleman" who was actively complicating the situation.
A Growing Trend of "Remediation" Fraud
The prosecution of Juan Ricardo Palacio Escobar is not an isolated incident but rather the latest in a series of aggressive U.S. Department of Justice (DoJ) actions targeting a new breed of cyber-criminality: the fraudulent security consultant.
In October 2026, the DoJ charged Edward Dubrovsky, an executive at Canadian firm Cybersteward, with cyber extortion and conspiracy. Simultaneously, Zohar Pinhasi, CEO of MonsterCloud, faced similar charges after allegedly charging customers $19 million for "remediation" services while secretly paying hackers $8 million to unlock systems. Earlier in the year, Angelo Martino, a Florida-based negotiator, received a 70-month prison sentence for his direct collaboration with the Blackcat/ALPHV ransomware group, where he leaked sensitive client information to help hackers extort higher payments.

Implications for the Cybersecurity Industry
The implications of this fraud are profound. For small and medium-sized businesses, the damage goes beyond the financial loss of the ransom. By relying on fraudulent firms, victims lose valuable time—the most critical factor in recovery—and inadvertently provide threat actors with more leverage. Furthermore, the use of remote access software like Anydesk by these "remediation" firms creates a massive security risk, potentially exposing sensitive data to the very actors they are supposedly fighting.
Experts argue that these cases underscore a critical failure in the regulatory oversight of the cybersecurity consulting sector. Unlike licensed professions such as law or accounting, the ransomware remediation industry remains largely unregulated, allowing bad actors to hide behind technical jargon and professional-looking websites.
The DoJ’s recent focus on these "double-agents" serves as a warning to both companies and the security community. The primary recommendation from federal agencies remains consistent: victims should engage only with established, verified incident response firms, preferably those with a proven track record and recognized credentials. Organizations are also urged to maintain air-gapped backups and avoid sharing details of their financial or negotiation strategies with any third party that cannot demonstrate total transparency in their operations.
As the legal proceedings against Palacio continue, the case serves as a stark reminder that in the high-stakes world of ransomware, the person offering a quick fix may be the greatest threat of all. The dismantling of RansomwareHelp is a significant victory for law enforcement, but it also highlights the urgent need for greater scrutiny of the "digital rescue" industry as it continues to evolve in response to the growing global ransomware crisis.