FBI Arrests Cybersecurity Executive in Connection with High-Profile ShinyHunters Data Breach Investigation

In a significant development that has sent shockwaves through the cybersecurity and cyber-insurance sectors, federal agents arrested a Canadian cybersecurity executive in Pennsylvania on Thursday. The arrest, confirmed by multiple sources close to the investigation, is directly tied to the expansive probe into the prolific hacking collective known as ShinyHunters. This group recently orchestrated a devastating breach against the Federal Bureau of Investigation (FBI), successfully exfiltrating sensitive personnel data, including medical and psychiatric records of agency staff.
The suspect, identified in federal court records as Edward Dobrovsky—with a minor spelling discrepancy from his professional profile—was apprehended while attending the Cyber Risk Summit at the Loews Philadelphia Hotel. The summit, which concluded on October 7, serves as a hub for industry leaders to discuss ransomware mitigation and extortion strategies. The arrest highlights an intensifying crackdown by federal authorities on individuals suspected of providing auxiliary support or facilitating communication for notorious cybercriminal syndicates.
Chronology of the Investigation
The apprehension of Dobrovsky is the latest in a series of aggressive maneuvers by the FBI to dismantle the infrastructure supporting ShinyHunters. The trajectory of this investigation has accelerated rapidly over the last several weeks:
- September 2026: Dutch law enforcement authorities, working in coordination with the FBI, arrested Pepijn van der Stap, a convicted cybercriminal previously linked to significant breaches. The seizure of digital devices during this operation provided the FBI with a roadmap of the group’s internal communications and operational tactics.
- Early October 2026: Following Van der Stap’s arrest, a secondary figure known as "Rey" assumed control of the ShinyHunters operation. In a brazen display of defiance, Rey taunted the FBI, leaking data pilfered from an internal bureau recruitment portal.
- October 7, 2026: Reports surfaced identifying "Rey" as Saif Al-din Khader, a teenager who had allegedly been detained and begun cooperating with federal authorities. This breakthrough occurred shortly after the group attempted to extort a digital aviation unit previously divested from Boeing.
- October 8, 2026: Federal agents apprehended Edward Dobrovsky in Philadelphia. Court records indicate he faces charges of conspiracy to threaten the confidentiality of information with the intent to extort money, as well as interference with commerce by threats.
- October 9, 2026: The case was officially transferred to the Eastern District of Texas, which has become the centralized command center for the federal investigation into the group’s activities.
The Role of Cybersecurity Professionals in Ransomware Negotiations
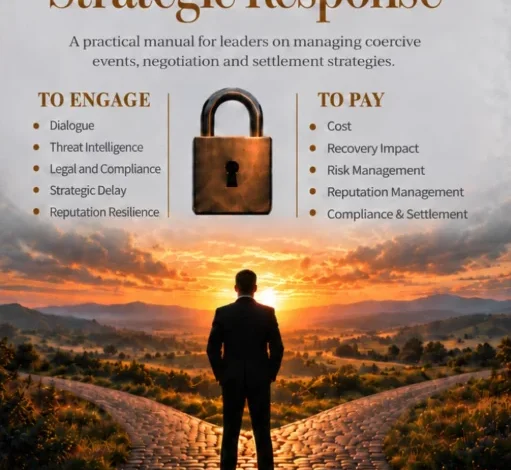
The arrest of a high-ranking executive within the ransomware negotiation space raises profound ethical and legal questions. Dobrovsky, a veteran of the industry, authored the book Cyber Extortion Strategic Response, which serves as a guide for organizations navigating the complexities of post-breach recovery. In his writing, Dobrovsky posited that engagement with criminal entities is a strategic necessity, arguing that "negotiating is not a commitment to pay," but rather a tool to "gather information, create time, and preserve options."

While many firms provide legitimate advisory services to companies under duress, the FBI’s investigation suggests that the line between professional negotiation and material support for criminal activity is being scrutinized more heavily than ever. If investigators can prove that intermediaries provided more than just advice—such as facilitating payments that violated federal sanctions or providing tactical guidance to hackers—it could redefine the legal landscape for cybersecurity firms globally.
Data Security Implications and Bureau Vulnerability
The breach of the FBI’s recruitment portal remains one of the most embarrassing security failures for the agency in recent years. By accessing files that included unit specializations, medical histories, and psychiatric evaluations, ShinyHunters compromised the safety of agents and their families. This level of exposure underscores a broader vulnerability: even agencies tasked with protecting national security are not immune to the sophisticated phishing and credential-harvesting campaigns employed by modern cyber-extortionists.
According to federal data, ShinyHunters has been responsible for the theft and extortion of more than $70 million from corporate and government entities in the first three quarters of 2026 alone. Their methodology—typically involving the exfiltration of sensitive data followed by the threat of public release—has become the gold standard for digital coercion.
Official Responses and Legal Standing
As of Friday morning, the FBI has declined to provide specific commentary on the arrest, citing the ongoing nature of the investigation. However, the move to consolidate the case in the Eastern District of Texas signals that the Justice Department is building a comprehensive case against a network of individuals rather than focusing solely on the hackers themselves.
A spokesperson for Cypfer, a firm previously associated with Dobrovsky, clarified that he had resigned from his position as a managing director in December 2025, distancing the firm from his current legal predicament. Similarly, representatives from CyberSteward, the firm Dobrovsky was representing at the Philadelphia conference, have not yet issued a formal statement regarding the charges.

As of the latest filing, Dobrovsky remains in federal custody. Court records confirm he has not yet been appointed legal counsel, and his initial appearance before a judge is pending.
Broader Impact on the Cyber-Insurance Industry
The broader implications of this case are likely to be felt across the insurance industry. Cyber-insurance providers have long relied on specialized firms to navigate ransom demands. The possibility that these intermediaries may be compromised or, in some cases, complicit in the schemes they are hired to thwart, creates a massive liability issue for insurers.
Industry analysts suggest that the "negotiation" sector may soon face stricter regulatory oversight. There is a growing consensus that the "agnostic" approach to extortion—whereby firms focus solely on the client’s recovery without considering the implications of funding criminal enterprises—is becoming increasingly untenable. If the Department of Justice successfully prosecutes this case, it will likely mandate a shift toward a more transparent, legally vetted process for handling ransomware incidents.
Future Outlook
The investigation is described by sources as "fast-moving," with further charges against additional individuals in the private sector expected in the coming weeks. The transition from catching the perpetrators to catching those who facilitate the aftermath of the crime marks a new, more aggressive phase in the war on digital extortion.
For the cybersecurity community, the arrest of a prominent, published author in the field serves as a stark warning: the tools and strategies used to "protect" victims are being subjected to the same level of forensic scrutiny as the attacks themselves. As the FBI continues to pore over the seized devices of the ShinyHunters collective, the industry awaits further clarity on where the boundary between professional service and criminal conspiracy truly lies. The upcoming proceedings in the Eastern District of Texas will likely become a landmark case in the history of international cybercrime law enforcement.