Cilium 1.20 marks a major milestone in cloud native networking and security for the Kubernetes ecosystem

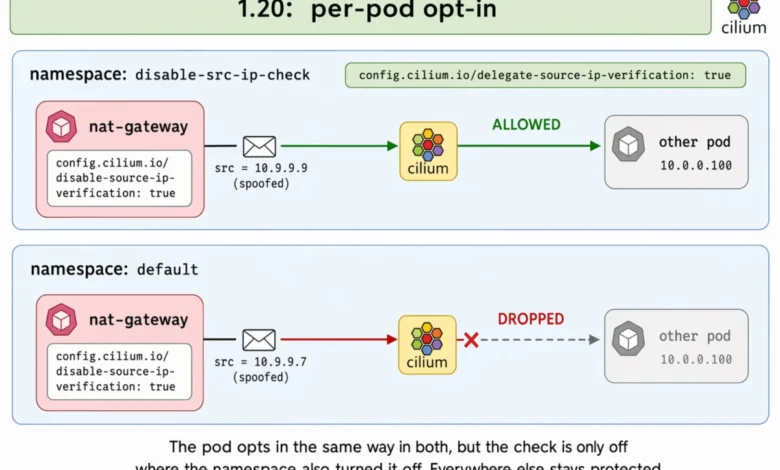
The release of Cilium 1.20, announced on September 14, 2026, by maintainers Nico Vibert and Donia Chaiehloudj, represents the second major update for the open-source project this year. Following the release of version 1.19, which solidified zTunnel and multi-pool IPAM, the 1.20 iteration introduces critical enhancements in networking, security, and day-to-day cluster operations. Supported by a diverse group of engineers from organizations including Datadog, Google, and Microsoft, this release aims to close longstanding feature gaps and improve the overall efficiency of containerized environments at scale.

Advancements in Networking and IP Management
A central achievement of the 1.20 release is the attainment of feature parity between IPv4 and IPv6 within the AWS ENI IPAM mode. This development effectively resolves a four-year-old feature request, allowing for the allocation of VPC-routable IPv6 addresses to pods via Prefix Delegation. For platform engineers, this eliminates a significant hurdle in adopting dual-stack networking on AWS EKS, as the Cilium operator now seamlessly attaches IPv6 /80 prefixes to node interfaces.
Beyond IP management, Cilium 1.20 brings performance optimizations through the "netkit" datapath. Originally touted as a paradigm shift for container networking, netkit bypasses the overhead associated with traditional virtual ethernet (veth) pairs. Previously, the requirement for a kernel version 6.8 or higher limited the deployment of netkit in mixed-environment clusters. The new "auto" configuration mode allows the Cilium agent to probe host kernels at startup, defaulting to netkit when supported and gracefully reverting to veth where it is not. This automation simplifies the adoption of high-performance networking across diverse hardware fleets.

Further enhancing the extensibility of the platform, the introduction of datapath plugins allows third-party developers to instrument the eBPF datapath without requiring patches to the core Cilium codebase. By enabling plugins to run as independent, versioned processes, the project reduces the maintenance burden on cloud providers and enterprises who previously had to manage custom forks of the Cilium agent to achieve specialized observability or security goals.
Refined Traffic Distribution and Load Balancing
Cilium 1.20 expands its service-level control, aligning more closely with the evolving Kubernetes Gateway API. The project now supports the standard trafficDistribution specification, including the PreferSameZone and PreferSameNode policies. These settings empower administrators to minimize latency and reduce cross-zone data transfer costs by ensuring that service traffic remains as close to the client as possible without sacrificing availability.

Additionally, the introduction of weighted EndpointSlices for Maglev-based load balancing provides a refined mechanism for traffic management. By applying a service.cilium.io/weight annotation, administrators can now perform connection-preserving drains of specific backends. By setting a weight to zero, backends are removed from the Maglev lookup table, allowing existing connections to complete while steering all new traffic elsewhere. This granular control is a notable improvement over previous "all-or-nothing" traffic distribution methods.
Strengthening Gateway API and Security
As the industry shifts toward the Gateway API, Cilium 1.20 continues its rapid integration, moving from v1.4 to v1.6. A primary addition is the implementation of the ExternalAuth filter. This allows for native north-south boundary authentication, where gateways can verify credentials against an external service—such as an OIDC provider or an internal authorization server—before allowing traffic to reach backend services. This integration facilitates a standardized approach to securing access for humans, CI/CD pipelines, and AI agents alike.

Security posture is further bolstered by the move toward "sidecarless" mutual TLS via zTunnel. By providing authentication and encryption in the traffic path, zTunnel effectively addresses the shortcomings of legacy mutual authentication methods, such as the initial packet drop and the lack of encryption for intra-node traffic. While zTunnel remains in beta, the 1.20 release provides improved configuration options, including support for SPIRE-based workload identity and new Prometheus metrics for monitoring connection health. The deprecation of the legacy mutual authentication feature signals the project’s clear commitment to the zTunnel architecture.
Furthermore, the implementation of Kubernetes ClusterNetworkPolicy (KCNP) provides a unified, cluster-scoped security model. By offering "Admin" and "Baseline" tiers, KCNP allows platform teams to enforce global security guardrails that supersede namespaced policies, a feature long requested by security-conscious organizations.

Operations and Scalability Improvements
Operational efficiency is a recurring theme in the 1.20 release. The binary size of the cilium-cni plugin has been reduced by approximately 80%, from 76 MB to 16 MB. This optimization significantly reduces the overhead associated with image pulling and installation across thousands of nodes.
The introduction of the cluster-mesh policy entity simplifies policy management for large-scale, multi-cluster deployments. Previously, administrators had to manually enumerate remote clusters or rely on complex label selectors to allow cross-cluster traffic. The new entity aggregates these identities, reducing the number of entries in the BPF policy map. This not only makes policy writing more intuitive but also ensures that performance remains stable as the cluster mesh grows.

In the realm of troubleshooting, the project has overhauled BGP tooling. The new hive-shell interface allows engineers to inspect BGP route policies and peer states directly from the Cilium agent. This addresses a common pain point for users operating in complex, self-managed environments who previously lacked granular visibility into BGP session health.
Broader Industry Impact and Chronology
The release of Cilium 1.20 follows a period of rapid institutional adoption. Major industry players, including OpenAI, Michelin, and Telefónica’s acens, have increasingly relied on Cilium to manage their cloud-native infrastructure. The project’s ability to standardize complex networking and security tasks has made it a preferred choice for organizations navigating the transition to multi-cluster and hybrid-cloud architectures.

The timing of this release, arriving in the second half of 2026, aligns with the broader Kubernetes community’s focus on maturing multi-cluster service discovery and standardizing security APIs. By promoting the Multi-Cluster Services (MCS) API implementation to a stable level, the Cilium project is aligning itself with the vendor-neutral standards championed by the Kubernetes SIG-multicluster group. This move is expected to simplify the migration process for users who wish to utilize portable, standard APIs while maintaining the high-performance benefits of the eBPF-based datapath.
Implications and Future Outlook
The implications of Cilium 1.20 are significant for enterprises aiming to reduce technical debt while increasing security. By consolidating various networking and security features into a single platform—often replacing the need for multiple disparate tools—Cilium 1.20 allows for a more cohesive operational model. The focus on "auto" configurations and standardized APIs like the Gateway API suggests a long-term strategy of reducing the complexity associated with Kubernetes networking.

As the Cilium community looks ahead, the upcoming Developer Summit at KubeCon + CloudNativeCon North America in Salt Lake City, scheduled for November 2026, will serve as a platform for further technical discourse and the sharing of production-grade experiences. For organizations already operating at scale, the improvements in policy map aggregation and binary footprint reduction are timely, addressing the inevitable performance degradation that often accompanies cluster growth.
In conclusion, Cilium 1.20 represents more than just a collection of new features; it is a strategic step toward a more robust, standardized, and performant cloud-native future. By prioritizing backward compatibility where possible and aggressively pursuing standard APIs where necessary, the maintainers have provided a clear path forward for both small-scale deployments and global-scale infrastructure providers. The shift toward zTunnel, the maturation of Gateway API support, and the refinement of policy management underscore a project that is not only keeping pace with the industry but is actively setting the standard for container networking.
Related posts: