Russian Enterprises Under Siege by NightEagle Hacking Cat and Toy Ghouls Threat Activity Clusters

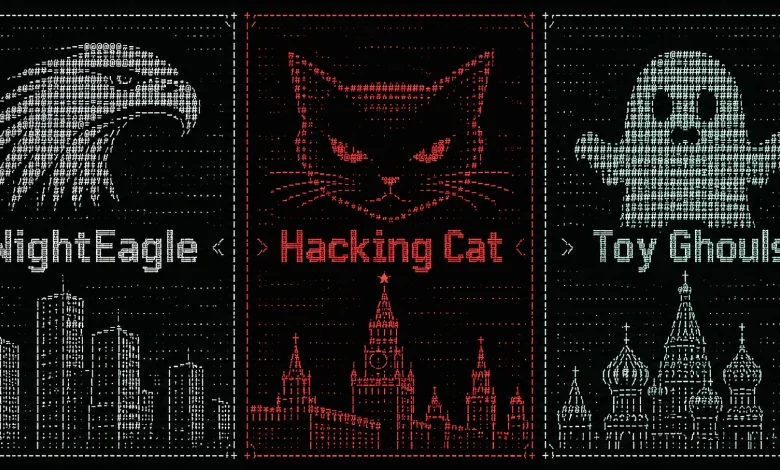
The digital landscape within the Russian Federation has faced a significant escalation in targeted cyber aggression, with security researchers at Kaspersky identifying three distinct threat activity clusters—NightEagle, Hacking Cat, and Toy Ghouls—that have systematically compromised corporate and governmental infrastructure. These groups, each employing unique methodologies ranging from sophisticated modular backdoors to destructive wiper malware, represent a shifting paradigm in the regional threat environment. While the motivations behind these clusters vary from espionage to hacktivism and financial gain, their collective impact on Russian network security has prompted a heightened state of alert among domestic cybersecurity professionals.
The Rise of NightEagle: Espionage and Persistence
NightEagle, also tracked under the designation APT-Q-95, has demonstrated a high degree of technical proficiency since emerging on the threat landscape in 2023. Unlike opportunistic attackers, NightEagle maintains a strategic focus on persistence and deep network penetration. Kaspersky’s latest intelligence indicates that the group’s primary vector for initial access involves the exploitation of compromised valid credentials, specifically targeting corporate Virtual Private Networks (VPNs).
The operational security of NightEagle is notably robust. Attackers have been observed routing their VPN connections through the Russian segment via Cloudflare WARP tunnels, while simultaneously masking their origins through European virtual infrastructure providers. This geographic obfuscation is designed to circumvent IP-based blocking and geolocation filters commonly employed by corporate firewalls.
Once inside the perimeter, NightEagle deploys GhostContainer, a sophisticated modular backdoor. This tool provides the operators with near-total control over Microsoft Exchange Servers. By masquerading as legitimate server components, GhostContainer effectively blends into the background of standard server operations, allowing for long-term data exfiltration and command execution. The technical sophistication of the malware is further evidenced by its integration of publicly available open-source tools, such as the Neo-reGeorg tunnel and various ysoserial utility components.
The group’s lateral movement strategy is equally methodical. NightEagle utilizes legitimate administrative tools, including Microsoft dev tunnels and the open-source rdp2tcp utility, to redirect traffic and move through internal networks. By exploiting vulnerabilities in Active Directory—most notably the BlueKeep (CVE-2019-0708) vulnerability—the attackers can escalate privileges, create rogue local administrator accounts, and execute DCSync attacks to impersonate domain controllers. The long-term objective of these efforts is to harvest domain credentials and maintain access via long-lived Kerberos tickets, effectively compromising the integrity of an organization’s entire identity management infrastructure.
Hacking Cat: From Hacktivism to Destructive Warfare
In a stark departure from the espionage-heavy tactics of NightEagle, the entity known as Hacking Cat represents a more aggressive, ideologically driven threat. Active since February 2024, this pro-Ukrainian hacktivist group initially focused on website defacements and low-level data breaches. However, by late 2025, the group’s operational tempo shifted toward high-impact, destructive cyber warfare.

Hacking Cat operates within a loose coalition of regional hacktivist entities, often collaborating with the Cyber Anarchy Squad and the Ukrainian Cyber Alliance. This environment makes precise attribution difficult, as the groups frequently share infrastructure, custom malware toolkits, and target lists. The transition from simple defacement to the deployment of complex ransomware and wiper malware marks a significant evolution in their capabilities.
The group utilizes vulnerabilities in Exchange servers, such as CVE-2021-26855, to deploy Gorilla RAT, a Go-based remote access trojan. Gorilla RAT serves as the group’s Swiss Army knife, allowing for real-time interaction with infected systems, file exfiltration, and the establishment of persistent TCP tunnels. When the objective shifts from espionage to destruction, Hacking Cat deploys a suite of ransomware families, including the "Monkey" variant.
Monkey ransomware is notable for its cross-platform compatibility, targeting Windows, Linux, and VMware ESXi environments. The malware is written in a diverse array of programming languages, including Rust, .NET, and C++. Analysis of the Rust-based variants suggests a high level of sophistication, utilizing ChaCha20-Poly1305 encryption to lock victim files. In some instances, the lack of a decryption key functionality—despite the presence of a ransom note—indicates that the "ransomware" is, in practice, a wiper tool designed for permanent data destruction.
Security analysts have noted a peculiar carelessness in some of the group’s Golang-based tools, such as the inclusion of functionality to remove shadow volume copies—a feature that is ineffective on Linux and ESXi systems. This observation has led researchers to hypothesize that these hacktivist groups are increasingly leveraging AI-assisted coding tools to expedite the development of their malware, occasionally leading to redundant or illogical code structures.
Toy Ghouls: The Shift Toward Bespoke Tooling
The third cluster, Toy Ghouls, also known as Bearlyfy or Feral Wolf, represents a financially motivated threat actor that has undergone a rapid professionalization of its operations. Initially reliant on leaked builders from established ransomware gangs like Babuk and LockBit, the group has transitioned to developing its own custom-built infrastructure.
Since mid-2026, Toy Ghouls has moved away from commodity ransomware in favor of a custom backdoor known as "Bird Agent." This backdoor is distributed via Windows Remote Management (WinRM), utilizing tools like Evil-WinRM and WinRM-fs for delivery. The Bird Agent is highly specialized, binding its configuration file to the specific MachineGuid of a victim’s system, ensuring that the malware cannot be easily analyzed in a sandboxed or virtualized environment.
The communication architecture of Bird Agent is particularly innovative. Rather than relying on traditional command-and-control (C2) domains, the malware utilizes the HiveMQ MQTT broker and the Matrix-based Element messenger. By funneling command traffic through these common, legitimate services, Toy Ghouls makes it significantly more difficult for network defenders to detect anomalous outbound traffic. The Element-based variant, in particular, demonstrates the group’s ability to turn collaborative platforms into clandestine command channels, where the malware acts as an endpoint participant in a Matrix room.

Chronology of Escalation
The intensification of these attacks follows a documented timeline:
- 2023: Initial emergence of the NightEagle group, focusing on initial reconnaissance and credential harvesting.
- February 2024: Hacking Cat begins operations, primarily through public-facing defacements and early-stage data leaks.
- July 2025: A notable spike in GhostContainer activity is observed, with NightEagle targeting government agencies and tech companies across the region.
- Late Summer 2025: The first instances of Monkey ransomware are documented, marking the beginning of the destructive shift in hacktivist tactics.
- July 2026: Toy Ghouls debuts the Bird Agent backdoor, signaling a move toward custom-built, highly evasive tooling.
Broader Implications and Defense Analysis
The emergence of these three distinct clusters highlights a fundamental change in the threat landscape for Russian enterprises. The democratization of malware development, fueled by the availability of open-source projects and the potential misuse of generative AI, has allowed even disparate groups to maintain high-functioning attack toolkits.
For the victims, the implications are severe. The shift toward destructive "wiper-as-ransomware" tactics means that organizations can no longer rely on traditional incident response plans that prioritize restoration over data integrity. Furthermore, the use of legitimate administrative tools—such as WinRM and dev tunnels—makes the identification of "living-off-the-land" attacks increasingly difficult for standard Endpoint Detection and Response (EDR) solutions.
Security experts emphasize that these attacks demand a more granular approach to internal network segmentation. Given the reliance on Active Directory exploits, the principle of "least privilege" is now more critical than ever. Organizations are being advised to move toward a Zero Trust architecture, where internal movement is as strictly monitored and authenticated as external access.
While Hacking Cat has publicly denied responsibility for certain ransomware variants identified by Kaspersky, the broader consensus among intelligence providers is that the lines between independent hacktivist groups, state-aligned actors, and profit-driven cyber-criminals are blurring. As these groups refine their custom backdoors and improve their evasion techniques, the burden on the defense community to stay ahead of the curve is reaching unprecedented levels. The focus for Russian enterprises must now shift toward proactive hunting and the hardening of identity management systems, as these appear to be the primary targets for the next generation of regional cyber threats.
Related posts: