Global Cybersecurity Infrastructure Faces Unprecedented Strain as Supply Chain Vulnerabilities and Nation-State Espionage Converge


The intersection of artificial intelligence integration, systemic supply chain vulnerabilities, and geopolitical espionage has created an exceptionally volatile landscape for global cybersecurity infrastructure. Over recent weeks, a convergence of critical reports—spanning malicious software extensions, sophisticated nation-state tracking operations, unvetted access to secure government networks, and systemic operating system vulnerabilities—has underscored the fragility of modern digital defenses. Cybersecurity researchers, intelligence analysts, and industry experts are increasingly warning that the foundational architecture of the global internet is buckling under the weight of rapid deployment models and a lack of rigorous, localized security protocols.
Supply Chain Incursions and Malicious AI Extensions
The weaponization of developer ecosystems reached a new milestone as security researchers at Phorion and OpenSourceMalware uncovered a targeted campaign involving a malicious extension for Claude Code on Cursor. Attackers successfully embedded a sophisticated JavaScript loader at the very beginning of the extension’s primary execution script (extension.js), leaving the legitimate software’s downstream functionality completely intact to avoid immediate detection.
According to technical breakdowns provided by the investigating firms, the malicious payload was designed to establish persistent Secure Shell (SSH) backdoors on compromised machines. However, a series of coding errors within the malware’s initialization routines ultimately neutralized its broader effectiveness. The script failed to dynamically enable SSH services on Windows and macOS systems where the protocol was not already actively running, leaving the reverse tunnels incapable of establishing remote access to the targeted devices.
Despite the operational failure of this specific campaign, security analysts emphasize that the incident highlights a severe structural risk: the implicit trust developers place in third-party extensions and AI-assisted coding environments. As organizations increasingly adopt AI-driven development tools to accelerate software delivery, the attack surface expands exponentially, allowing threat actors to leverage supply chain entry points that bypass traditional perimeter security defenses.
Geopolitical Pressure, Semiconductor Intelligence, and Export Controls
Simultaneously, geopolitical tensions surrounding advanced artificial intelligence hardware have intensified following disclosures regarding high-level intelligence omissions. Reports surfaced detailing how political leadership allegedly sidelined intelligence briefings concerning a covert Chinese intelligence operation targeting the Chief Executive Officer of Nvidia, Jensen Huang. The operation reportedly involved an individual named Huang Le, who maintained a close professional relationship with the Nvidia CEO while operating as an executive at Megaspeed, a firm marketing itself as an AI cloud datacenter provider.
The investigation revealed significant anomalies surrounding Megaspeed’s operations. Deliveries of high-end Nvidia hardware components to the company’s facilities remained uninstalled and crated, appearing staged for outward shipment rather than operational deployment. Furthermore, structural transparency regarding the firm proved elusive; corporate filings indicated that Megaspeed’s Singapore-based director, James Tan, resided permanently in China and was virtually absent from regional administrative oversight.
Analysts note that these intelligence blind spots directly intersect with broader policy debates regarding the relaxation of export controls designed to restrict Beijing’s access to advanced semiconductors. Observers suggest that the prioritization of short-term market stability and corporate stock performance over rigorous national security vetting creates critical vulnerabilities within the global technology supply chain, allowing foreign intelligence entities to cultivate high-level access near foundational infrastructure providers.
Federal Network Security and Institutional Oversight Challenges
Domestic cybersecurity governance has faced similar scrutiny following a series of alarming incidents involving unvetted third-party integrations and federal transparency roadblocks. A notable breach of operational protocol occurred when a contractor working for Accenture connected an artificial intelligence agent directly to the Pentagon’s secure network, inadvertently transmitting sensitive defense-related data to an external, high-risk website. Cybersecurity professionals immediately classified the incident as a critical national security threat, pointing to the inherent dangers of deploying autonomous AI agents within classified environments without strict data-loss prevention controls.
Compounding these concerns, federal agencies have reportedly stonewalled the Government Accountability Office (GAO) during comprehensive audits assessing the data security practices of the Department of Government Efficiency (DOGE). The lack of institutional cooperation has raised alarms among congressional watchdogs, who argue that opaque data handling protocols and rapid structural reorganizations within federal entities foster a lax security culture. This unmeasured approach increases the likelihood of data exfiltration, poor access control enforcement, and the transfer of confidential government records to insecure cloud infrastructure.
Operating System Flaws and Persistent Login Vulnerabilities
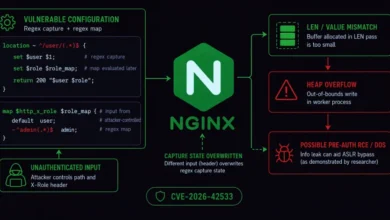
At the software level, foundational operating systems continue to suffer from legacy design flaws that facilitate privilege escalation. Security disclosures this month highlighted a critical vulnerability in systems running the musl C library, where attackers could achieve root access by flooding authentication prompts with excessively long passwords—a modern variation of input-handling bugs that have plagued Unix-like environments for decades.
Parallel disclosures from threat intelligence firms detailed systemic vulnerabilities across major mobile and desktop platforms. Google faced criticism after declining to patch the "GhostMap" issue and a remote-triggerable APK compression vulnerability in Android, which malicious actors utilized to force target devices into continuous bootloops without user interaction. Security researchers warn that these persistent flaws, combined with the exploitation of compromised Tor exit nodes to intercept unencrypted email and redirect SSH communications, demonstrate that endpoint hardening remains inadequate across consumer and enterprise markets.
Economic and Strategic Implications of Automated Workforce Reduction
Beyond direct technical exploits, economists and technologists are sounding the alarm over the broader societal and economic fallout driven by aggressive artificial intelligence adoption. The rapid push by corporate leadership to automate white-collar administrative and software-engineering roles has given rise to what researchers term "The AI Layoff Trap."
According to mathematical models developed by academic researchers, corporations are systematically eliminating human workforces under the assumption that large language models and autonomous agents can indefinitely substitute for human labor. However, economists warn of a fundamental macroeconomic contradiction: by laying off massive segments of the workforce, companies simultaneously erode their own consumer base. Without sustained wage generation, the broader market experiences a contraction in purchasing power, threatening a systemic economic tailspin.
Furthermore, analysts point out that automated code generation often results in "code cutting" rather than true software engineering, leading to a proliferation of poorly understood, insecure software artifacts that exacerbate the global cybersecurity crisis. As organizations grapple with the dual pressures of automated integration and intensifying state-sponsored cyber operations, the imperative for robust, energy-gapped security segregation and rigorous regulatory oversight has never been more urgent.