FBI Arrests Cybersecurity Executive in Connection with High-Profile ShinyHunters Data Breach Investigation

In a dramatic escalation of the federal government’s pursuit of the notorious cybercrime syndicate known as ShinyHunters, FBI agents apprehended a prominent Canadian cybersecurity executive in Pennsylvania on Thursday. The arrest comes as part of an expansive, multi-jurisdictional investigation into the group, which recently gained international infamy for infiltrating an FBI recruitment portal and compromising the sensitive personal, medical, and psychiatric records of thousands of federal agents.
The suspect, identified in federal court records as Edward Dobrovsky—a figure deeply embedded in the professional sphere of ransomware negotiation and digital extortion advisory—was taken into custody while attending the Cyber Risk Summit at the Loews Philadelphia Hotel. His arrest represents a significant pivot in the FBI’s strategy to dismantle the infrastructure supporting large-scale digital extortion operations.
The Scope of the Allegations
According to court filings indexed at CourtListener, the defendant is facing grave charges, including conspiracy to threaten the confidentiality of information with the intent to extort, and interference with commerce by threats. While much of the primary complaint remains under seal, the charges reflect a growing federal determination to criminalize the "gray area" services often provided by private firms that facilitate ransom payments.
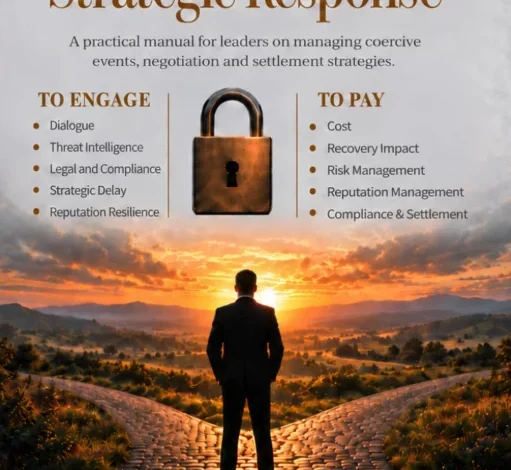
The suspect, a 54-year-old industry veteran, is the author of the 2026 text Cyber Extortion Strategic Response, a manual that purports to guide organizations through the complex, high-stakes environment of dealing with criminal hackers. In his professional capacity, he has frequently argued that communication with threat actors is a tactical necessity rather than a capitulation. However, federal prosecutors now allege that such engagement crossed the legal threshold into criminal conspiracy.
A Timeline of the ShinyHunters Investigation
The arrest of the Canadian executive is the latest link in a fast-moving chain of events that has kept the federal cybersecurity community in a state of high alert throughout late 2026.

- Late 2025: ShinyHunters intensifies its operations, pivoting toward software-as-a-service (SaaS) providers to siphon corporate credentials.
- September 2026: Dutch law enforcement officials arrest Pepijn van der Stap, a convicted cybercriminal linked to the group’s inner circle. The FBI subsequently secures and begins analyzing seized devices from this operation.
- October 7, 2026: Reports emerge detailing the apprehension of "Rey," identified as a teenager named Saif Al-din Khader, who had taken control of the group following Van der Stap’s arrest. Khader is reportedly cooperating with investigators.
- October 8, 2026: Edward Dobrovsky is arrested in Philadelphia during the Cyber Risk Summit.
- October 9, 2026: Legal proceedings are formally moved to the Eastern District of Texas, a venue that has emerged as the central hub for the FBI’s broader ShinyHunters task force.
The Professional Intersection of Security and Crime
The investigation has cast a harsh spotlight on the "ransomware negotiation" industry. Firms that specialize in these services often operate in a precarious regulatory environment. Their business model—facilitating payments to hackers to secure the release of stolen data or the restoration of encrypted systems—has long been criticized by federal agencies for potentially fueling the growth of cyber-extortion ecosystems.
The suspect was a prominent figure at the Cyber Risk Summit, an event that serves as a cornerstone for insurers, legal professionals, and security experts. His association with the firm CyberSteward and his past involvement with the Canadian security company Cypfer highlights how deeply the lines between "white-hat" security consulting and the underworld of digital negotiation have blurred.
In a clarification following the arrest, a spokesperson for Cypfer noted that the suspect was not a founder of their organization, as his LinkedIn profile had previously indicated, but rather a former managing director who resigned in December 2025. This discrepancy in the suspect’s professional history underscores the volatility and lack of transparency often present in the rapidly expanding cyber-insurance sector.
Broader Implications and Federal Policy
The FBI’s decision to centralize the prosecution in the Eastern District of Texas signals that the government is treating the ShinyHunters case not merely as a series of isolated hacks, but as a systemic threat to national security. The theft of data from the FBI’s own recruitment portal—which contained specialized information on agents, including their unit placements and psychological evaluations—marked a turning point in the bureau’s resolve.
With ShinyHunters having allegedly extorted more than $70 million from victims in 2026 alone, the federal government is under immense pressure to prove that it can hold those who assist or facilitate these crimes accountable. Experts suggest that the indictment of an executive who specializes in "strategy and settlement services" serves as a warning to the private sector: the government is no longer content with targeting only the hackers themselves, but is moving to disrupt the entire supply chain of the ransomware economy.
Challenges in Legal Precedent
The case against the defendant promises to be a landmark legal battle regarding the boundaries of corporate crisis management. If prosecutors successfully argue that his actions constituted conspiracy to commit extortion, it could drastically alter how insurance firms and incident response teams handle ransomware demands.

Currently, the suspect remains in federal custody. The absence of legal representation in the initial court filings suggests a high level of complexity in the defense, as the intersection of international cybersecurity law, the Foreign Corrupt Practices Act, and domestic extortion statutes will likely form the basis of the proceedings.
Looking Ahead
As the investigation continues, federal sources indicate that additional charges against other principals at companies specializing in ransomware negotiations may be forthcoming. The FBI’s success in flipping high-level members of the ShinyHunters hierarchy, such as the operative known as "Rey," has provided investigators with a roadmap of the group’s internal communications and financial ledger.
The cybersecurity community remains divided on the fallout of these arrests. While some applaud the aggressive stance taken by the FBI to curb the payment of ransoms, others worry that by criminalizing the negotiation process, the government may inadvertently leave victimized corporations with no path to recovery, potentially increasing the total financial damage caused by future breaches.
For now, the focus remains on the courtroom in Texas. As more information is unsealed, the trial is expected to provide unprecedented insight into the hidden world of ransomware negotiations and the precarious relationship between the security professionals who manage these crises and the criminal syndicates that create them. The FBI has declined to provide further comment, citing the ongoing nature of the investigation, but the message to the industry is clear: the era of unchecked mediation with cyber-extortionists is rapidly coming to an end.
Related posts: