Citrix NetScaler Zero-Day Vulnerabilities Exploited in the Wild Trigger Urgent Patching Requirements

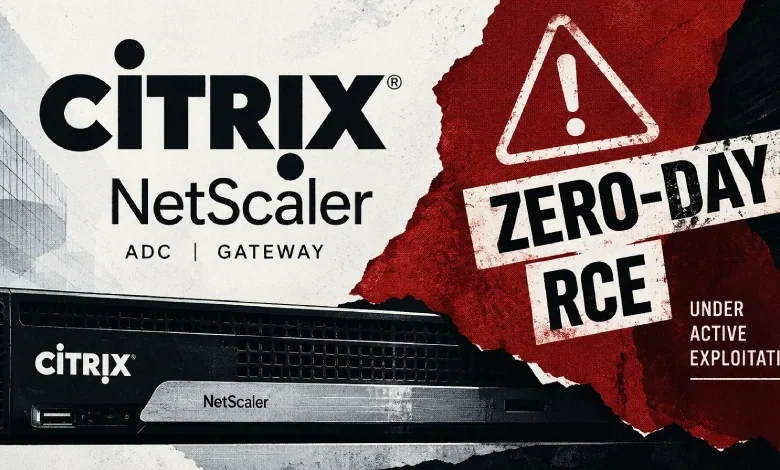
Two critical remote code execution (RCE) vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway have been confirmed as the targets of active exploitation, prompting an urgent security advisory from the software vendor. The discovery, which came to light on September 27, 2026, involves two high-severity flaws that allow unauthenticated attackers to gain unauthorized control over enterprise network infrastructure. Citrix has released emergency security patches to address these vulnerabilities, alongside six additional, less critical flaws, and is urging all customers to prioritize immediate deployment.
The severity of the situation is underscored by the fact that at least one of the two exploited vulnerabilities affects all deployments of the software, including those running default configurations. Because these flaws were actively exploited in the wild before a patch was made available, organizations that have not yet applied the latest updates are potentially already compromised.
Chronology of the Discovery
The timeline leading up to the official security bulletin suggests a rapid escalation of threats. On September 26, 2026, the security research firm watchTowr alerted the cybersecurity community to rumors of multiple unpatched RCE vulnerabilities affecting NetScaler appliances. The firm noted that, while specific technical details were initially scarce, the intelligence behind the rumors was highly credible.
By the early hours of September 27, reports began circulating on platforms such as Reddit, where IT administrators noted that their security providers had preemptively advised them to take their NetScaler appliances offline to prevent potential breach scenarios. Citrix officially acknowledged the two exploited vulnerabilities later that same day, confirming that CVE-2026-88771 and CVE-2026-88772 were being utilized by threat actors to compromise unmitigated systems.
This rapid sequence of events reflects a growing trend in the threat landscape where high-value edge infrastructure—such as load balancers, VPN gateways, and authentication servers—is being targeted with zero-day exploits to gain deep access into corporate and government networks.
The Scope of the Vulnerabilities
NetScaler ADC and NetScaler Gateway are cornerstones of modern enterprise network architecture. They function at the perimeter of the network, managing mission-critical tasks including secure remote access (VPN), load balancing for high-availability applications, and centralized user authentication. Because these devices sit between the public internet and internal corporate resources, any vulnerability that grants remote code execution capability is classified as a "tier-one" security emergency.

The current situation is complicated by the fact that many organizations remain on legacy or unsupported builds. Notably, the fix for the new vulnerabilities comes shortly after the 13.1 branch of NetScaler firmware reached its "End of Maintenance" milestone on September 15, 2026. While Citrix has provided patches for this branch, the transition underscores the difficulty organizations face in maintaining long-term security for complex edge appliances.
Furthermore, the affected versions include those that were recently updated to address a different authentication bypass vulnerability (CVE-2026-19490) in August. This suggests a persistent effort by threat actors to find new entry points within the same software ecosystem, potentially indicating that the codebase is being subjected to intense scrutiny by malicious entities.
Official Guidance and Mitigation Strategies
Citrix has not yet released specific indicators of compromise (IoCs) or detailed threat intelligence regarding the identity of the attackers or the duration of the campaign. In the absence of this data, the company has focused its guidance on immediate remediation. Organizations are advised to update their appliances to the latest available builds, which include the necessary security hardening.
However, security experts warn that for appliances that were potentially exposed to the internet prior to the patch, simply applying the update may be insufficient. Because these vulnerabilities allow for remote code execution, attackers may have already established "persistence" on the device—meaning they have installed backdoors, web shells, or compromised administrative credentials that will remain active even after the software vulnerability is patched.
Drawing on lessons learned from the 2025 exploitation of Citrix flaws in the Netherlands, the Dutch National Cyber Security Centre (NCSC) has previously advised that patching is only the first step in incident response. Administrators are urged to:
- Conduct a thorough forensic analysis of system logs and core dumps.
- Check for unauthorized changes to system configuration or newly created administrator accounts.
- Utilize specialized scripts to scan for persistent files or malicious binaries that might have been dropped by an attacker.
- Perform a comprehensive password and session token reset for all users and service accounts that passed through the affected gateway.
Broader Implications for Enterprise Security
The recurring nature of vulnerabilities in Citrix and similar edge-computing devices highlights a structural risk in modern IT operations. As organizations consolidate their security and connectivity functions into single, high-performance appliances, they inadvertently create "single points of failure." A single RCE vulnerability in a gateway device can provide an attacker with an instant foothold into an entire internal network, bypassing perimeter firewalls and traditional endpoint security.
The lack of public indicators of compromise in this specific case creates a dangerous "blind spot" for incident response teams. When a vulnerability is exploited as a zero-day, the traditional indicators—such as known malicious IP addresses or specific exploit signatures—are often missing, as attackers use novel methods to penetrate the system.

This event serves as a stark reminder of the "assumed compromise" model of security. In modern environments, organizations must operate under the assumption that their most critical edge devices could be compromised at any time. This necessitates robust network segmentation, the implementation of zero-trust architectures, and the continuous monitoring of administrative access patterns.
Future Outlook and Research
As of this writing, the cybersecurity industry is awaiting further details from researchers and the vendor. The interaction between the two exploited vulnerabilities and the six other flaws patched in the same update cycle remains a subject of investigation. It is possible that these vulnerabilities could be chained together to achieve more complex attack objectives, such as privilege escalation followed by lateral movement within the network.
The cybersecurity community remains on high alert. Companies relying on Citrix NetScaler are encouraged to:
- Audit External Exposure: Limit the accessibility of management interfaces to trusted IP addresses only.
- Monitor Traffic Patterns: Look for anomalous outbound traffic from the NetScaler appliance, which could indicate data exfiltration or a "phone home" signal to a command-and-control server.
- Review Lifecycle Management: Ensure that all appliances are within their support lifecycle, as end-of-life products are the most frequent targets for long-term exploitation.
The Cloud Software Group, which manages the Citrix brand, continues to work with security partners to analyze the scope of the attacks. Until a clearer picture of the threat actor’s capabilities is established, the prevailing advice from industry leaders is to treat all currently deployed, unpatched or recently patched NetScaler instances as potentially compromised, mandating a rigorous and transparent incident response procedure.
In conclusion, while the immediate risk is being addressed through emergency patching, the long-term integrity of these systems depends on the diligence of network administrators in conducting forensic sweeps and assuming a posture of proactive threat hunting. The event is a poignant example of the ongoing "cat-and-mouse" game between software vendors and sophisticated threat actors in the high-stakes environment of global enterprise infrastructure.